

Security Management, Monitored Daily
Ongoing monitoring, patching and incident response across your applications and infrastructure, whether cloud, on-premise, or both, so issues get caught and handled as they happen.
50+ ERP and software projects. Zero failed projects since 2021.
Security is not a task you finish once
New vulnerabilities appear after go-live, not before. Without an ongoing service watching for them, small issues sit unnoticed until they become incidents.
Monitoring that does not stop at go-live
Your applications and infrastructure are watched continuously, not checked on a schedule, so unusual activity gets flagged while it is still small.
- Coverage across cloud, on-premise or both.
- Alerts triaged by severity, not treated as equal.
- Every event kept in a running log.
Fixes applied, not just flagged
Known vulnerabilities get patched as part of the service rather than sitting in a backlog waiting for someone to schedule the work.
- Patches applied on a regular cycle.
- Higher-severity issues prioritized first.
- No separate ticket needed to get it scheduled.
Every event tracked from first alert to resolution
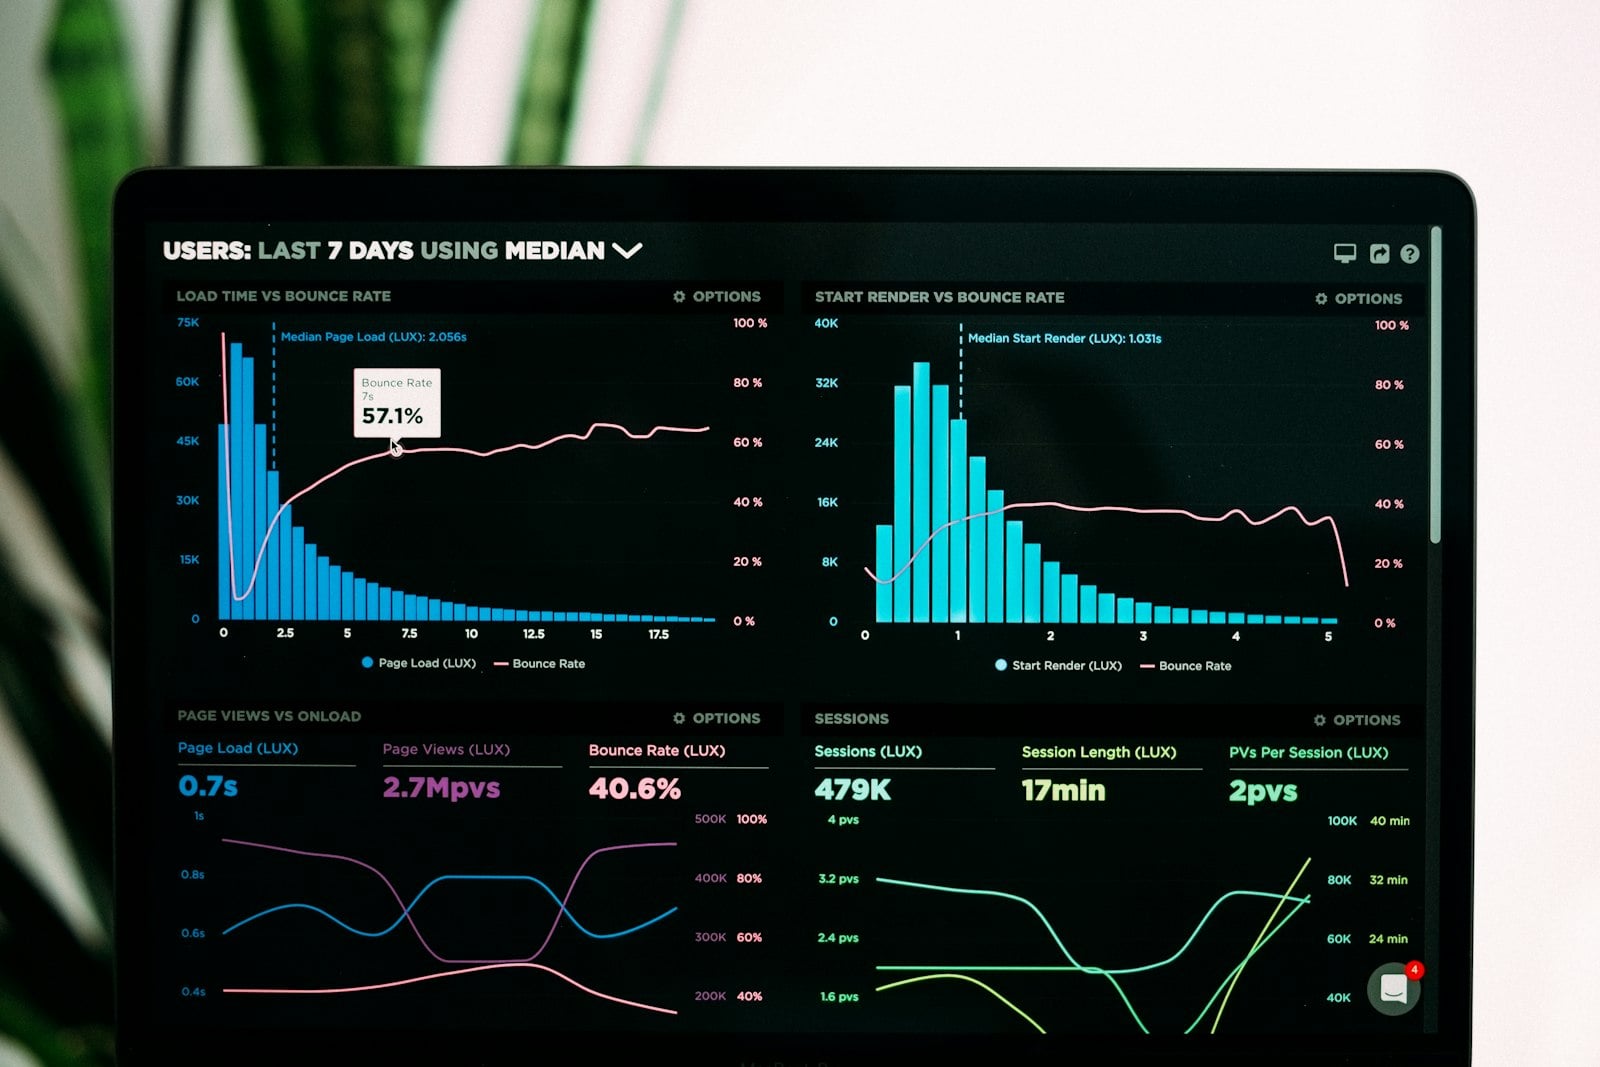
Illustrative example. Actual entries, severities and timestamps reflect your own monitored systems.
From a baseline assessment to ongoing coverage
Everything needed to keep systems watched and current
Continuous monitoring
Applications and infrastructure watched around the clock, not on a fixed schedule.
Patch management
Known vulnerabilities patched on a regular cycle rather than left in a backlog.
Incident response
Incidents worked from first alert through to resolution, with a clear record.
Severity triage
Every alert is graded by severity so the most urgent issues get attention first.
Cloud and on-premise
One service across whatever mix of cloud, on-premise or hybrid infrastructure you run.
Regular reporting
Reporting on what was monitored, patched and resolved, on an agreed cadence.
What Security Management changes day to day
Why teams trust TCB Infotech with Security Management
Security Management, answered
What does Security Management actually cover?
How is Security Management different from Cloud Security?
Do you cover on-premise infrastructure, or only the cloud?
How quickly do you respond to an incident?
Do you handle patching, or just monitoring and alerts?
What kind of reporting do we get?
Start Managing Security Day to Day
Monitoring, patching and incident response, set up across whatever infrastructure you run. Book a free consultation and walk through your current setup.
Book a Free Consultation →No commitment. See how coverage would apply to your systems first.
How Security Management Works
From a baseline assessment to daily monitoring, severity triage, patching and incident response. Here is how the service runs day to day.
Monitoring, triage and response, in that order
Set up across your entire environment
Monitoring is configured across your applications and infrastructure, whether that means cloud, on-premise, or a mix of both, so nothing is left unwatched.
- Coverage matched to what you actually run.
- Continuous, not checked on a fixed schedule.
- Every event kept in a running log.
Every alert triaged by severity
Alerts are graded Low, Medium or High as they come in, so a genuine incident is not sitting behind routine noise waiting to be noticed.
- Severity set at the point of alert.
- Higher-severity issues escalated first.
- Status tracked as Resolved, Monitoring or Investigating.
Fixes applied, not just flagged
Where a fix is available, it is applied directly as part of the service. Where an incident needs deeper investigation, it is worked through to resolution and logged.
- Patches applied on a regular cycle.
- Incidents tracked from alert to close.
- A reviewable record of what was done.
Everything included in the service
Continuous monitoring
Systems watched around the clock across your environment.
Patch management
Known vulnerabilities patched on a regular cycle.
Incident response
Incidents worked from first alert through to resolution.
Severity triage
Every alert graded so the most urgent issues get attention first.
Cloud and on-premise
One service across whatever infrastructure mix you run.
Regular reporting
Reporting on what was monitored, patched and resolved.